DFARS 7012 is in force — the SPRS score you affirm is a False Claims Act matter

Get On Track
Prepare For Engagement
Present Your Results
Capture Certification

Capture the contract with ConfiDense — the confidence is earned, the proof is yours.

Every new DoD contract that touches CUI rides on CMMC Level 2, and Every Control Counts.

ForteFide covers all 110 NIST 800-171 controls — auto-securing the technical controls and sealing signed, tamper-evident evidence your C3PAO can independently verify. Secure the rest by hand and we re-scan and sign the proof too — your evidence covers all 110, however it got secured. Everyone else stops at the paperwork; we secure what's vulnerable.
The part nobody warns you about
You self-assess and sign your SPRS score — under the False Claims Act.
A number you can’t back up isn’t a paperwork problem — it’s triple damages, a penalty on every invoice, and the person who signs personally on the hook. See how bad it gets — and how to sign a score you can prove.
See what’s at stake →
How it works

One path, start to finish.

Three moves, in order — each one carries into the next.

Step 1

Secure the Environment

We scan your systems and fix what’s broken — automatically.

Step 2

Know the Boundary

Where your CUI lives is your call, not ours. We assess the hosts you point us at — we never open a file.

Step 3

Hold the Line

They monitor. We fix — before drift becomes a finding.

Our Products

Compliance tools built to get you assessment-ready — and prove it.

Available Now

ForteFide

CMMC Level 2 / NIST 800-171 scanning, auto-remediation, and signed, tamper-evident evidence a C3PAO will accept. Scan your whole fleet, secure what’s vulnerable, and walk in with the proof your C3PAO needs.

ForteBase

Three products that answer what a compliance scan cannot: whether your controls actually hold, where your regulated data really sits, and what your AI tooling is exposing. Take them bundled or standalone — or plug ForteBase into ForteFide and run the whole suite from one place.

Explore ForteBase → See the full suite walkthrough →
Early Adopter

ForteStrike

A passing scan says a control is configured. It does not say it holds. ForteStrike runs the attack path against systems you own and reports which controls survived contact. Scope is agreed and fixed before anything runs, and every action is recorded against the engagement — so what comes back is evidence you can hand to an assessor, not an anecdote about a red-team week. In active development — get on the early-access list.
Early Adopter

ForteLock

ForteStrike finds the lock; ForteLock throws it. A continuous guard that adopts your approved exposure as a baseline, then reversibly contains any new, unauthorized port the moment it appears — no exploitation, containment only, fully reversible. The defensive sibling that keeps proven-closed controls closed, and ships control-mapped evidence for the boundary and monitoring families. In active development — get on the early-access list.
Early Adopter

DenseSense

Your assessment scope rests on one fact: which of your machines hold regulated data. Get that wrong and every control you pass is scored against the wrong boundary. The government has been settling cybersecurity False Claims Act cases against contractors since 2022, several running well into seven figures — and in at least one, the contractor maintained no data was ever lost. The exposure is the certification, not the breach. That's the question we're building DenseSense to answer from the disk instead of from memory: where controlled work actually sits, and where nothing controlled should ever be. It's in active development — get on the early-access list and we'll bring you in as soon as it's ready.
Early Adopter

DenseAIArmour

Your people are already using AI assistants, and the vendor keys they hand those assistants tend to sit in plaintext on the same machines you just had assessed. DenseAIArmour inventories that surface — local model endpoints, agent configurations, credentials at rest, and the AI vendor organization itself — and reports what it found. It also reports what it could not reach: anything outside its view is marked not assessed rather than passed, because a clean result you cannot trust is worse than no result at all. It reads; it changes nothing on your systems. In active development — get on the early-access list.
Early Adopter

DDVault + DDWitness

The evidence enclave. DDVault seals your compliance evidence with chain of custody — every artifact traceable to origin and provably untouched. DDWitness attests it is unaltered without ever holding the evidence itself. The custody layer beneath the suite’s signed evidence.
Coming soon

ForteFed — the finale

FedRAMP, the same way. Bring the ForteFide model — scan every control, secure what it can, seal signed evidence — to the federal cloud authorization that sits above CMMC. Not shipping yet: join the waitlist and help shape it.

See exactly where you stand — then prove it.

Struggling toward CMMC and dreading the “how do I show this to a C3PAO?” question? ForteFide scans your network, secures what it can, and produces the signed, tamper-evident evidence an assessor will accept — the proof is yours, ready for the assessment.

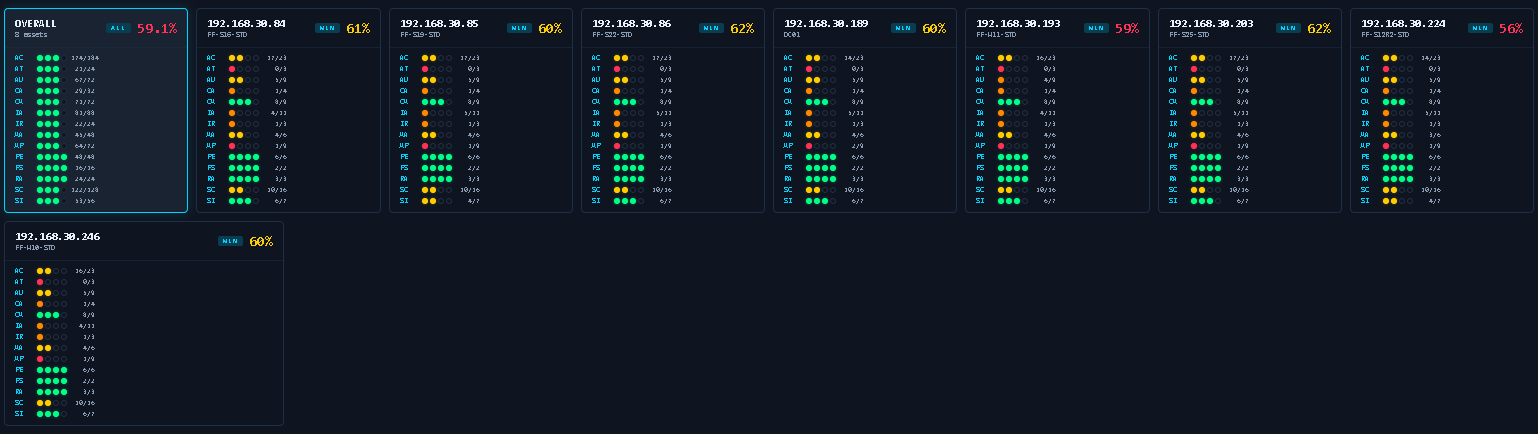
Per-target compliance scorecard across the fleet
1. See where you stand — same day
Scan your whole environment against 110 NIST 800-171 controls. Per-target scores, in plain sight — no weeks-long consultant assessment.
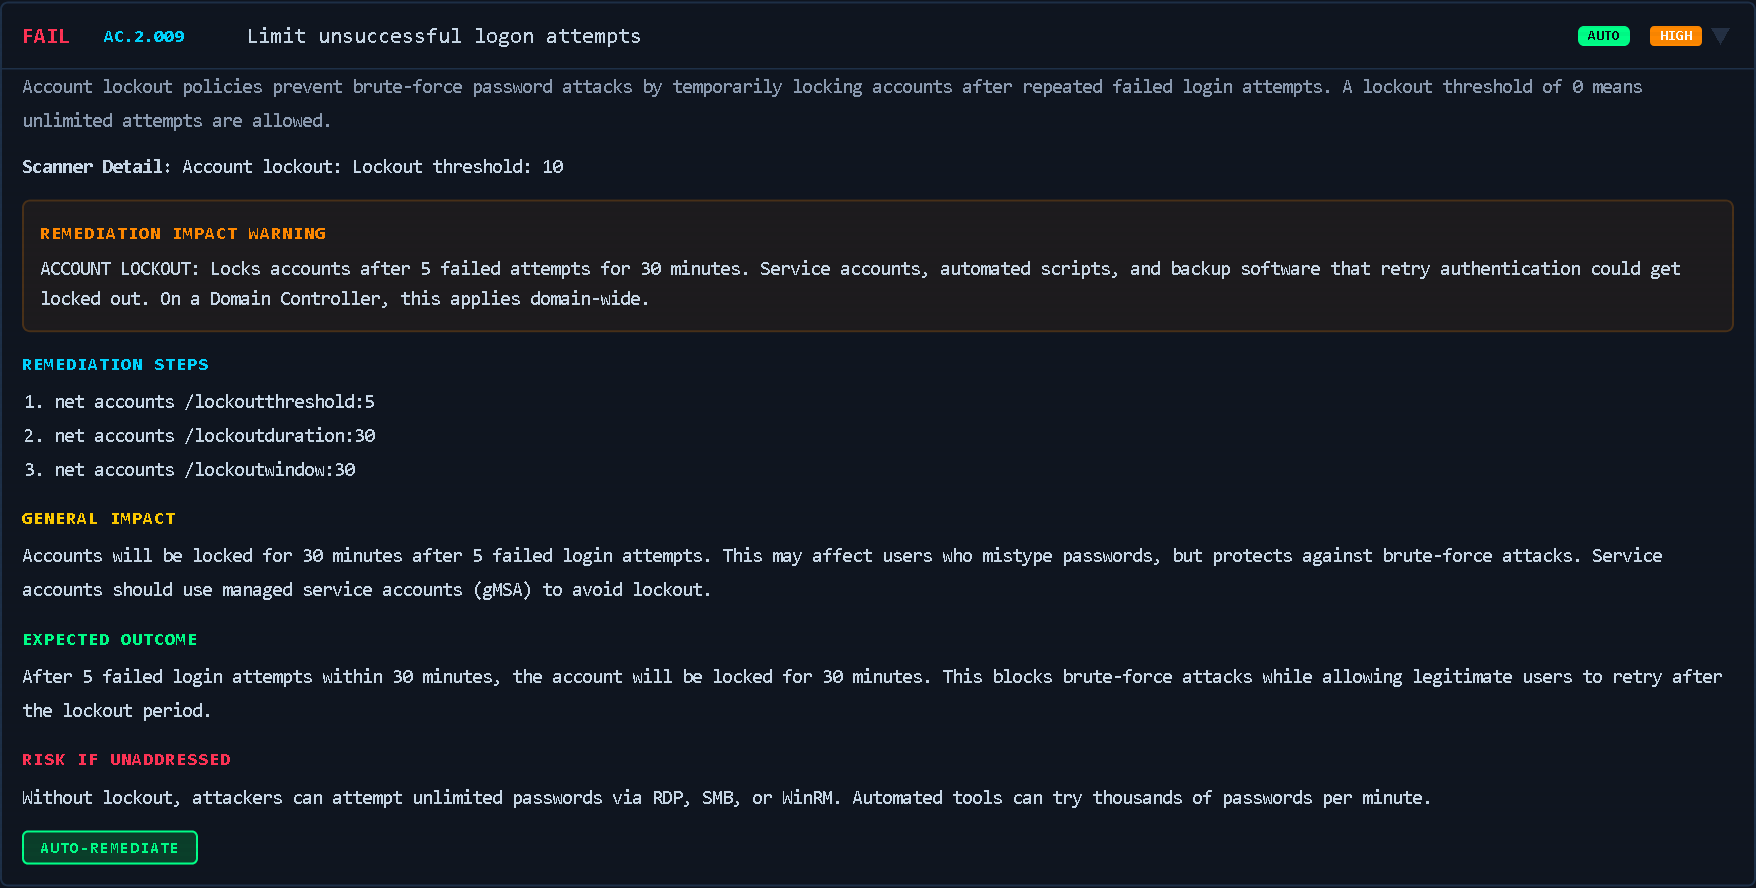
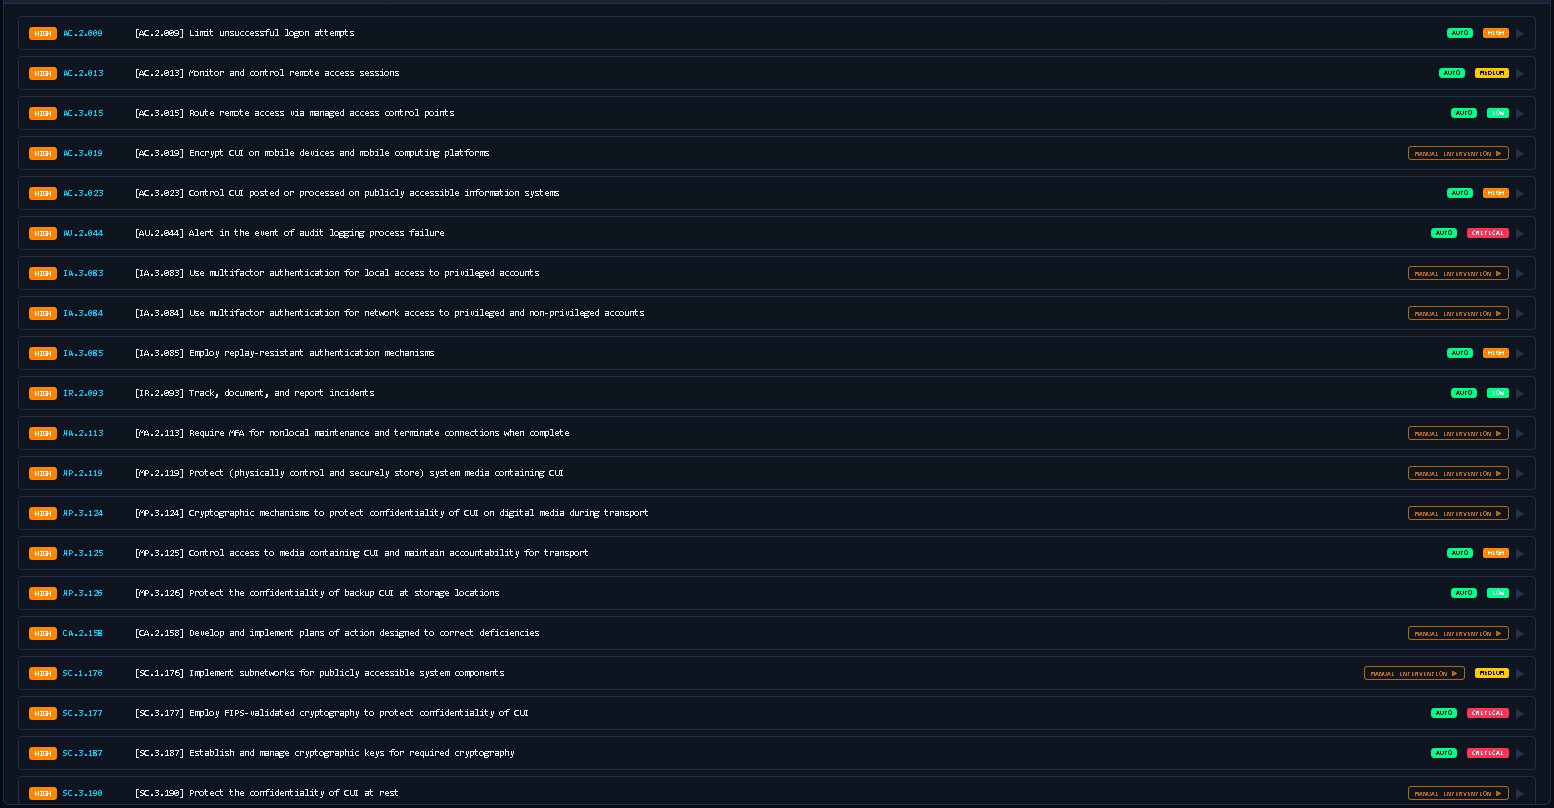
Plain-language findings list
2. Plain-language gaps
Every failed control, what it means, and how it gets secured — no consultant needed to translate the findings.
Per-control remediation steps, commands, and impact
3. Every change, in the open
Each control spells out the exact steps, commands, impact, and expected outcome before anything runs — then auto-remediate with one click. No black box.
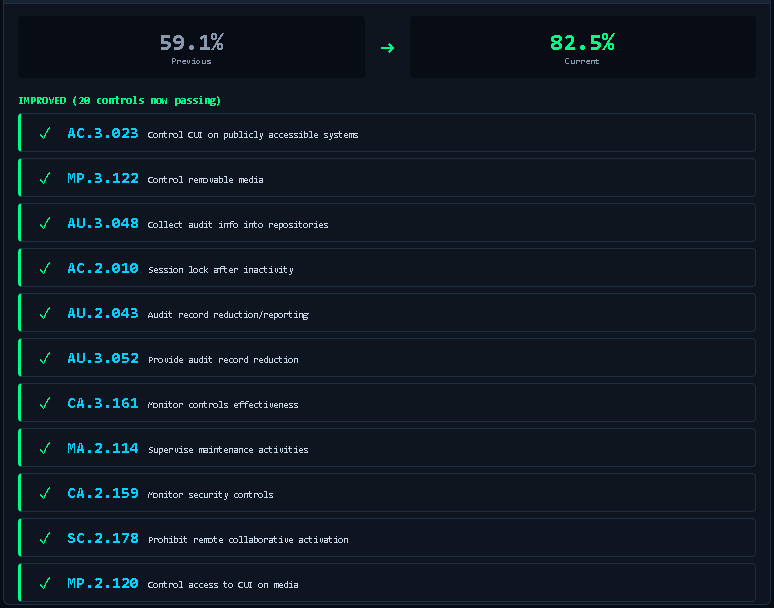
Compliance score before and after remediation
4. The proof a C3PAO accepts
Your score climbs as controls flip to passing — backed by a signed, tamper-evident evidence package with the full audit trail, independently verifiable. This is the evidence your C3PAO assessor accepts.

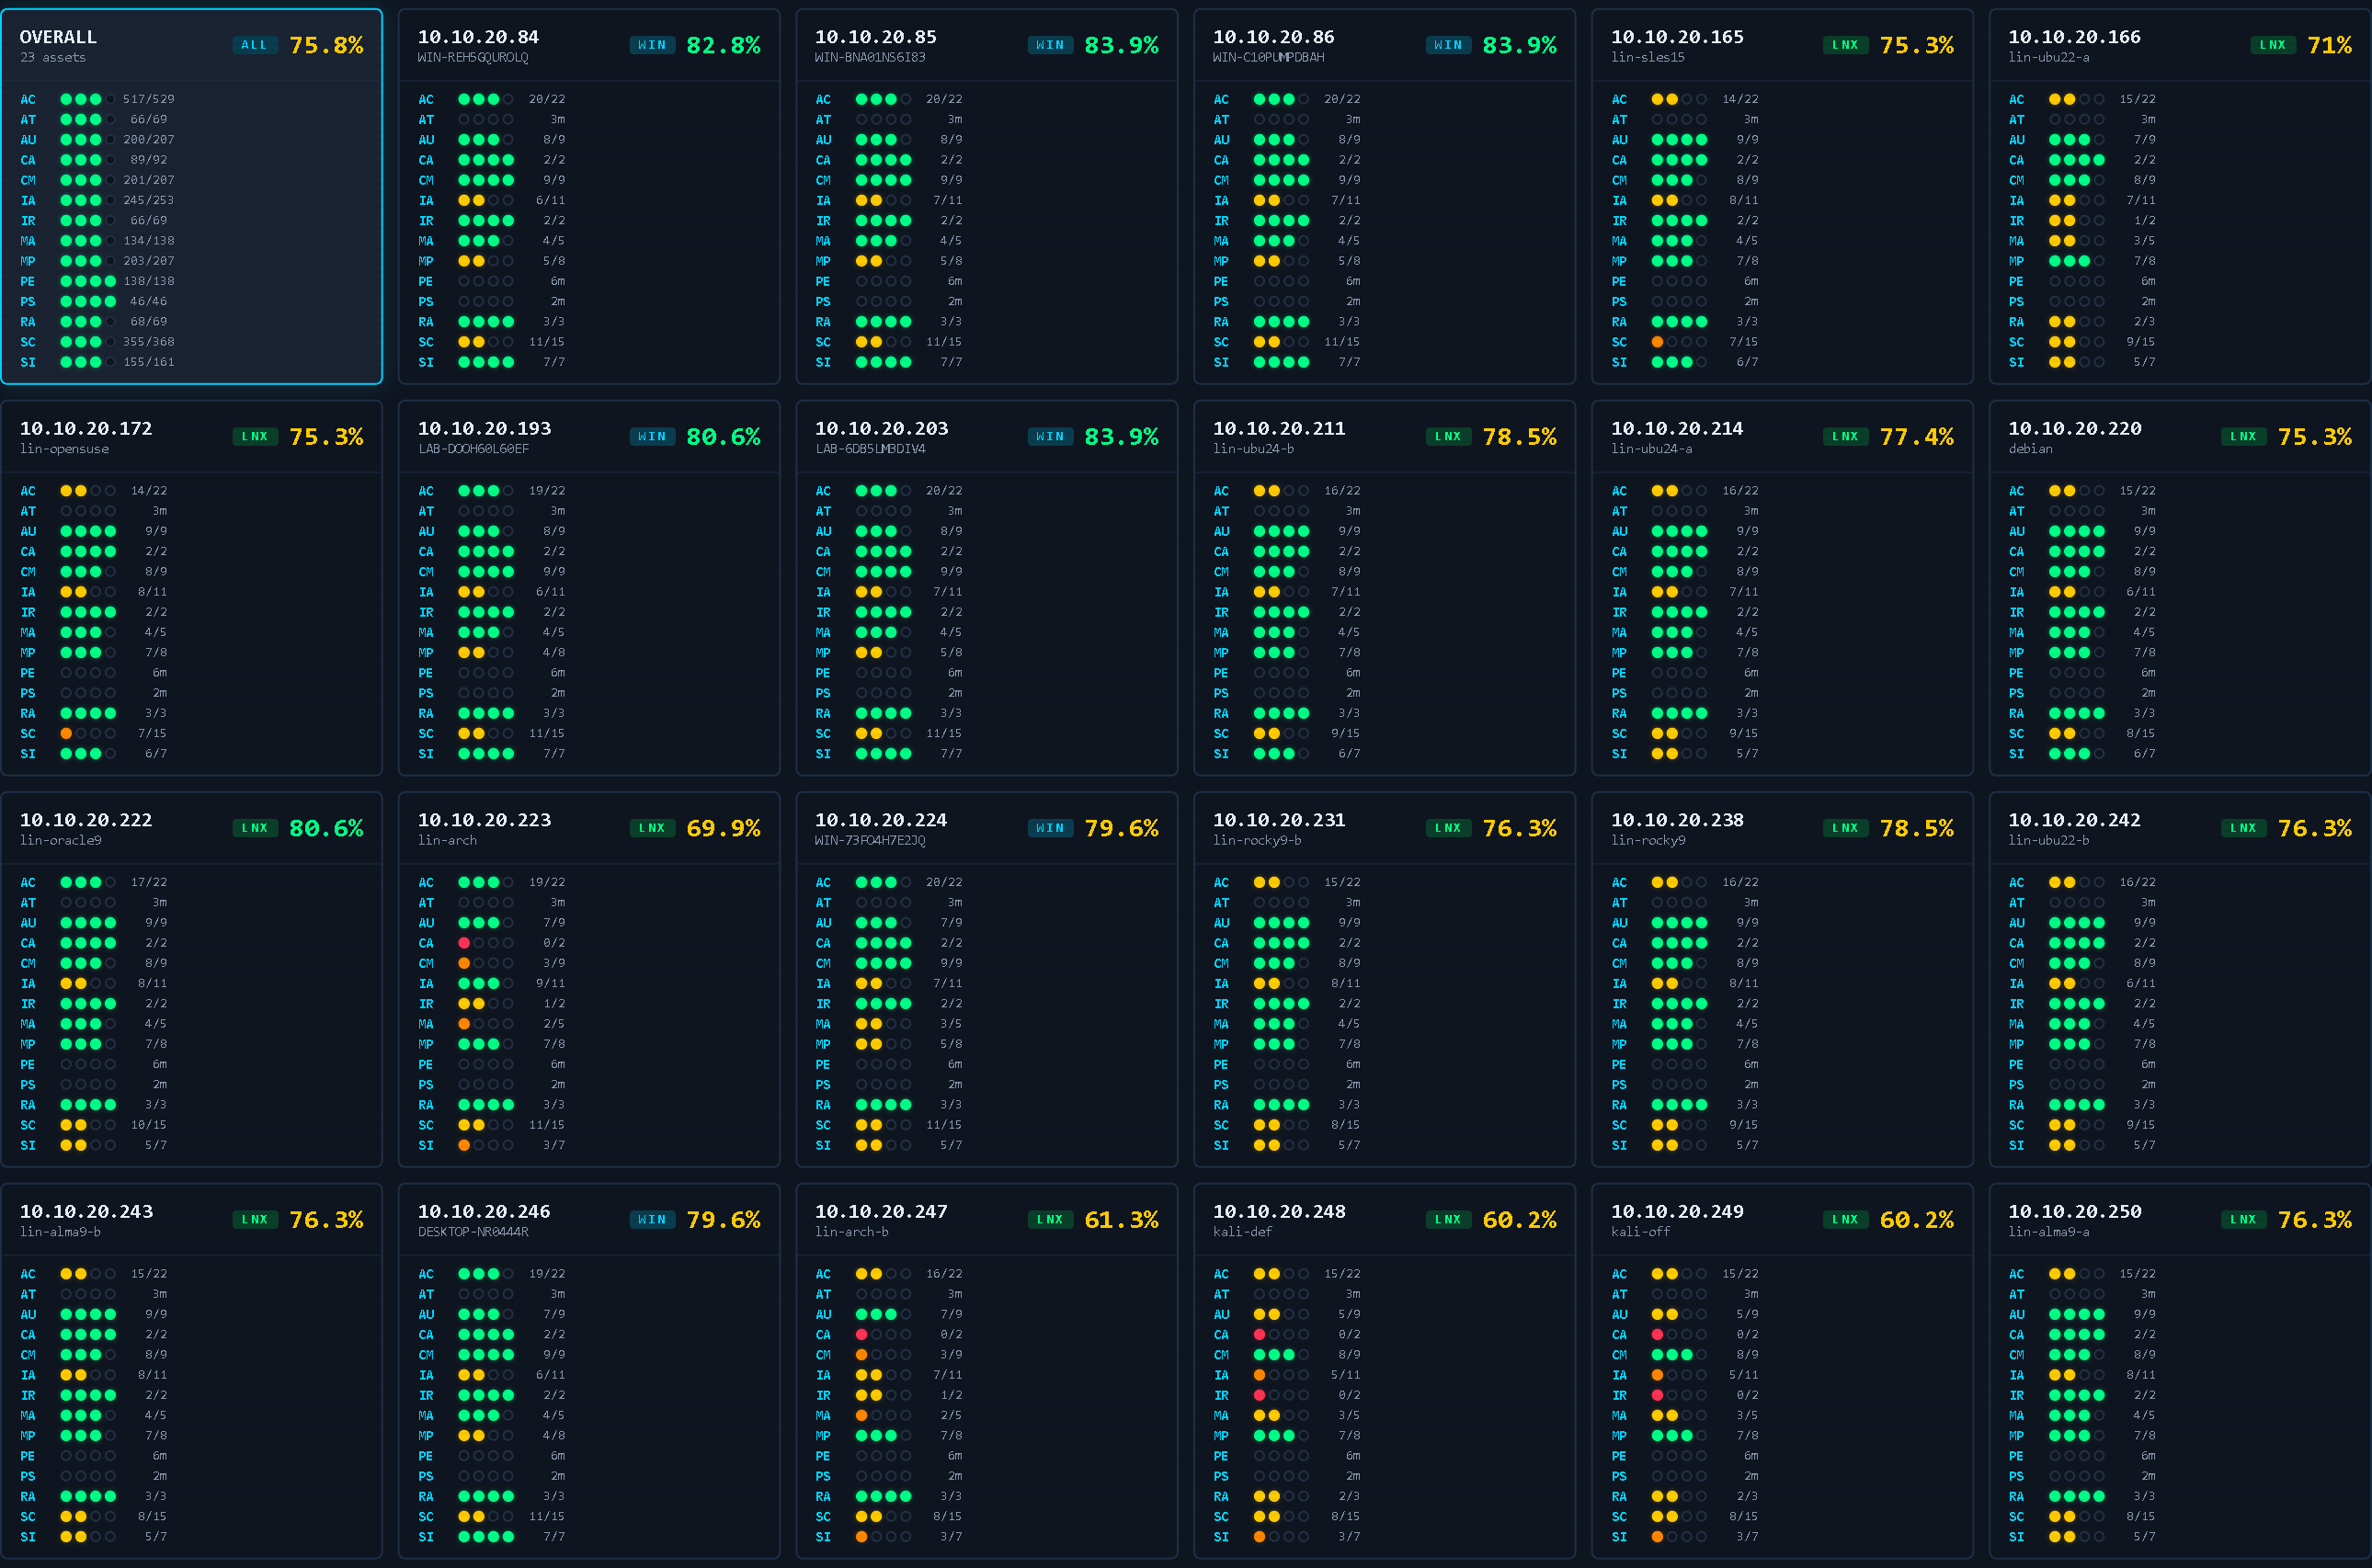
Your whole fleet — scored and hardened, target by target.

Not one machine, your entire environment. Every target evaluated against all 110 NIST 800-171 controls, before and after remediation — so nothing slips through, and you can prove it target by target.

Per-target compliance scores across the entire fleet

The math is not on your side. ForteFide is.

Few authorized assessors, a hard bar, and months of preparation. Here is what you are actually up against — and how ForteFide changes the math.

A day + assessor review
Getting CMMC-ready normally takes months of preparation. ForteFide scans your entire fleet against all 110 controls and hands you signed, verifiable evidence in about a day — so your SPRS score is backed by proof, not guesswork.
Under 100 C3PAOs
Fewer than 100 organizations nationwide are authorized to run a CMMC Level 2 assessment — against the tens of thousands of contractors in the DIB. If third-party assessments are reinstated, that line only gets longer, and it is first-come.
2 ports
Agentless by design. ForteFide assesses each target over the two management ports your admins already run — no agent to install on your targets.

Agentless by design

Most compliance platforms put a monitoring agent on every laptop and server you want covered — one more thing to deploy, approve, patch, and answer for at your next audit. ForteFide puts no agent on your targets: you run a single scanner, and it assesses each target over the remote-management service your admins already run:

Windows targets
WinRM enabled (TCP 5985, or 5986 for certificate auth).
Linux targets
SSH enabled (TCP 22).

Nothing to deploy, approve, or maintain on the targets themselves — you run a single scanner, and if those services are already running, ForteFide can assess the target.

All 110, not just the easy ones

Can't auto-secure it? You get the exact steps and a phased plan for every remaining control — guided remediation on all 110, not just the ones we can secure automatically. Secure it your way; ForteFide re-scans and seals the signed proof it's met, no matter who did the work.

What's next

Level 3 is coming

CMMC Level 3 is government-assessed (DIBCAC) and even more evidence-intensive. The signed-evidence discipline you build for Level 2 today is the foundation Level 3 will demand — no proof, more scrutiny.

This isn't a shortcut. It's the real thing.

We don't cut corners — we check the same 110 requirements the assessor checks, secure the ones we safely can, and produce cryptographically signed, tamper-evident evidence. Run the free scan once before an assessment, or every month to stay ready year-round. The proof is always there, always verifiable, always yours. When the assessor asks how you did it, you hand them the signed evidence and the standalone verifier.

×Enlarged screenshot