ForteFide
Scanner, remediation engine, and signed evidence producer for CMMC Level 2 — every package carries a tamper-evident Ed25519 signature your assessor verifies offline, with no callback and no license key required.
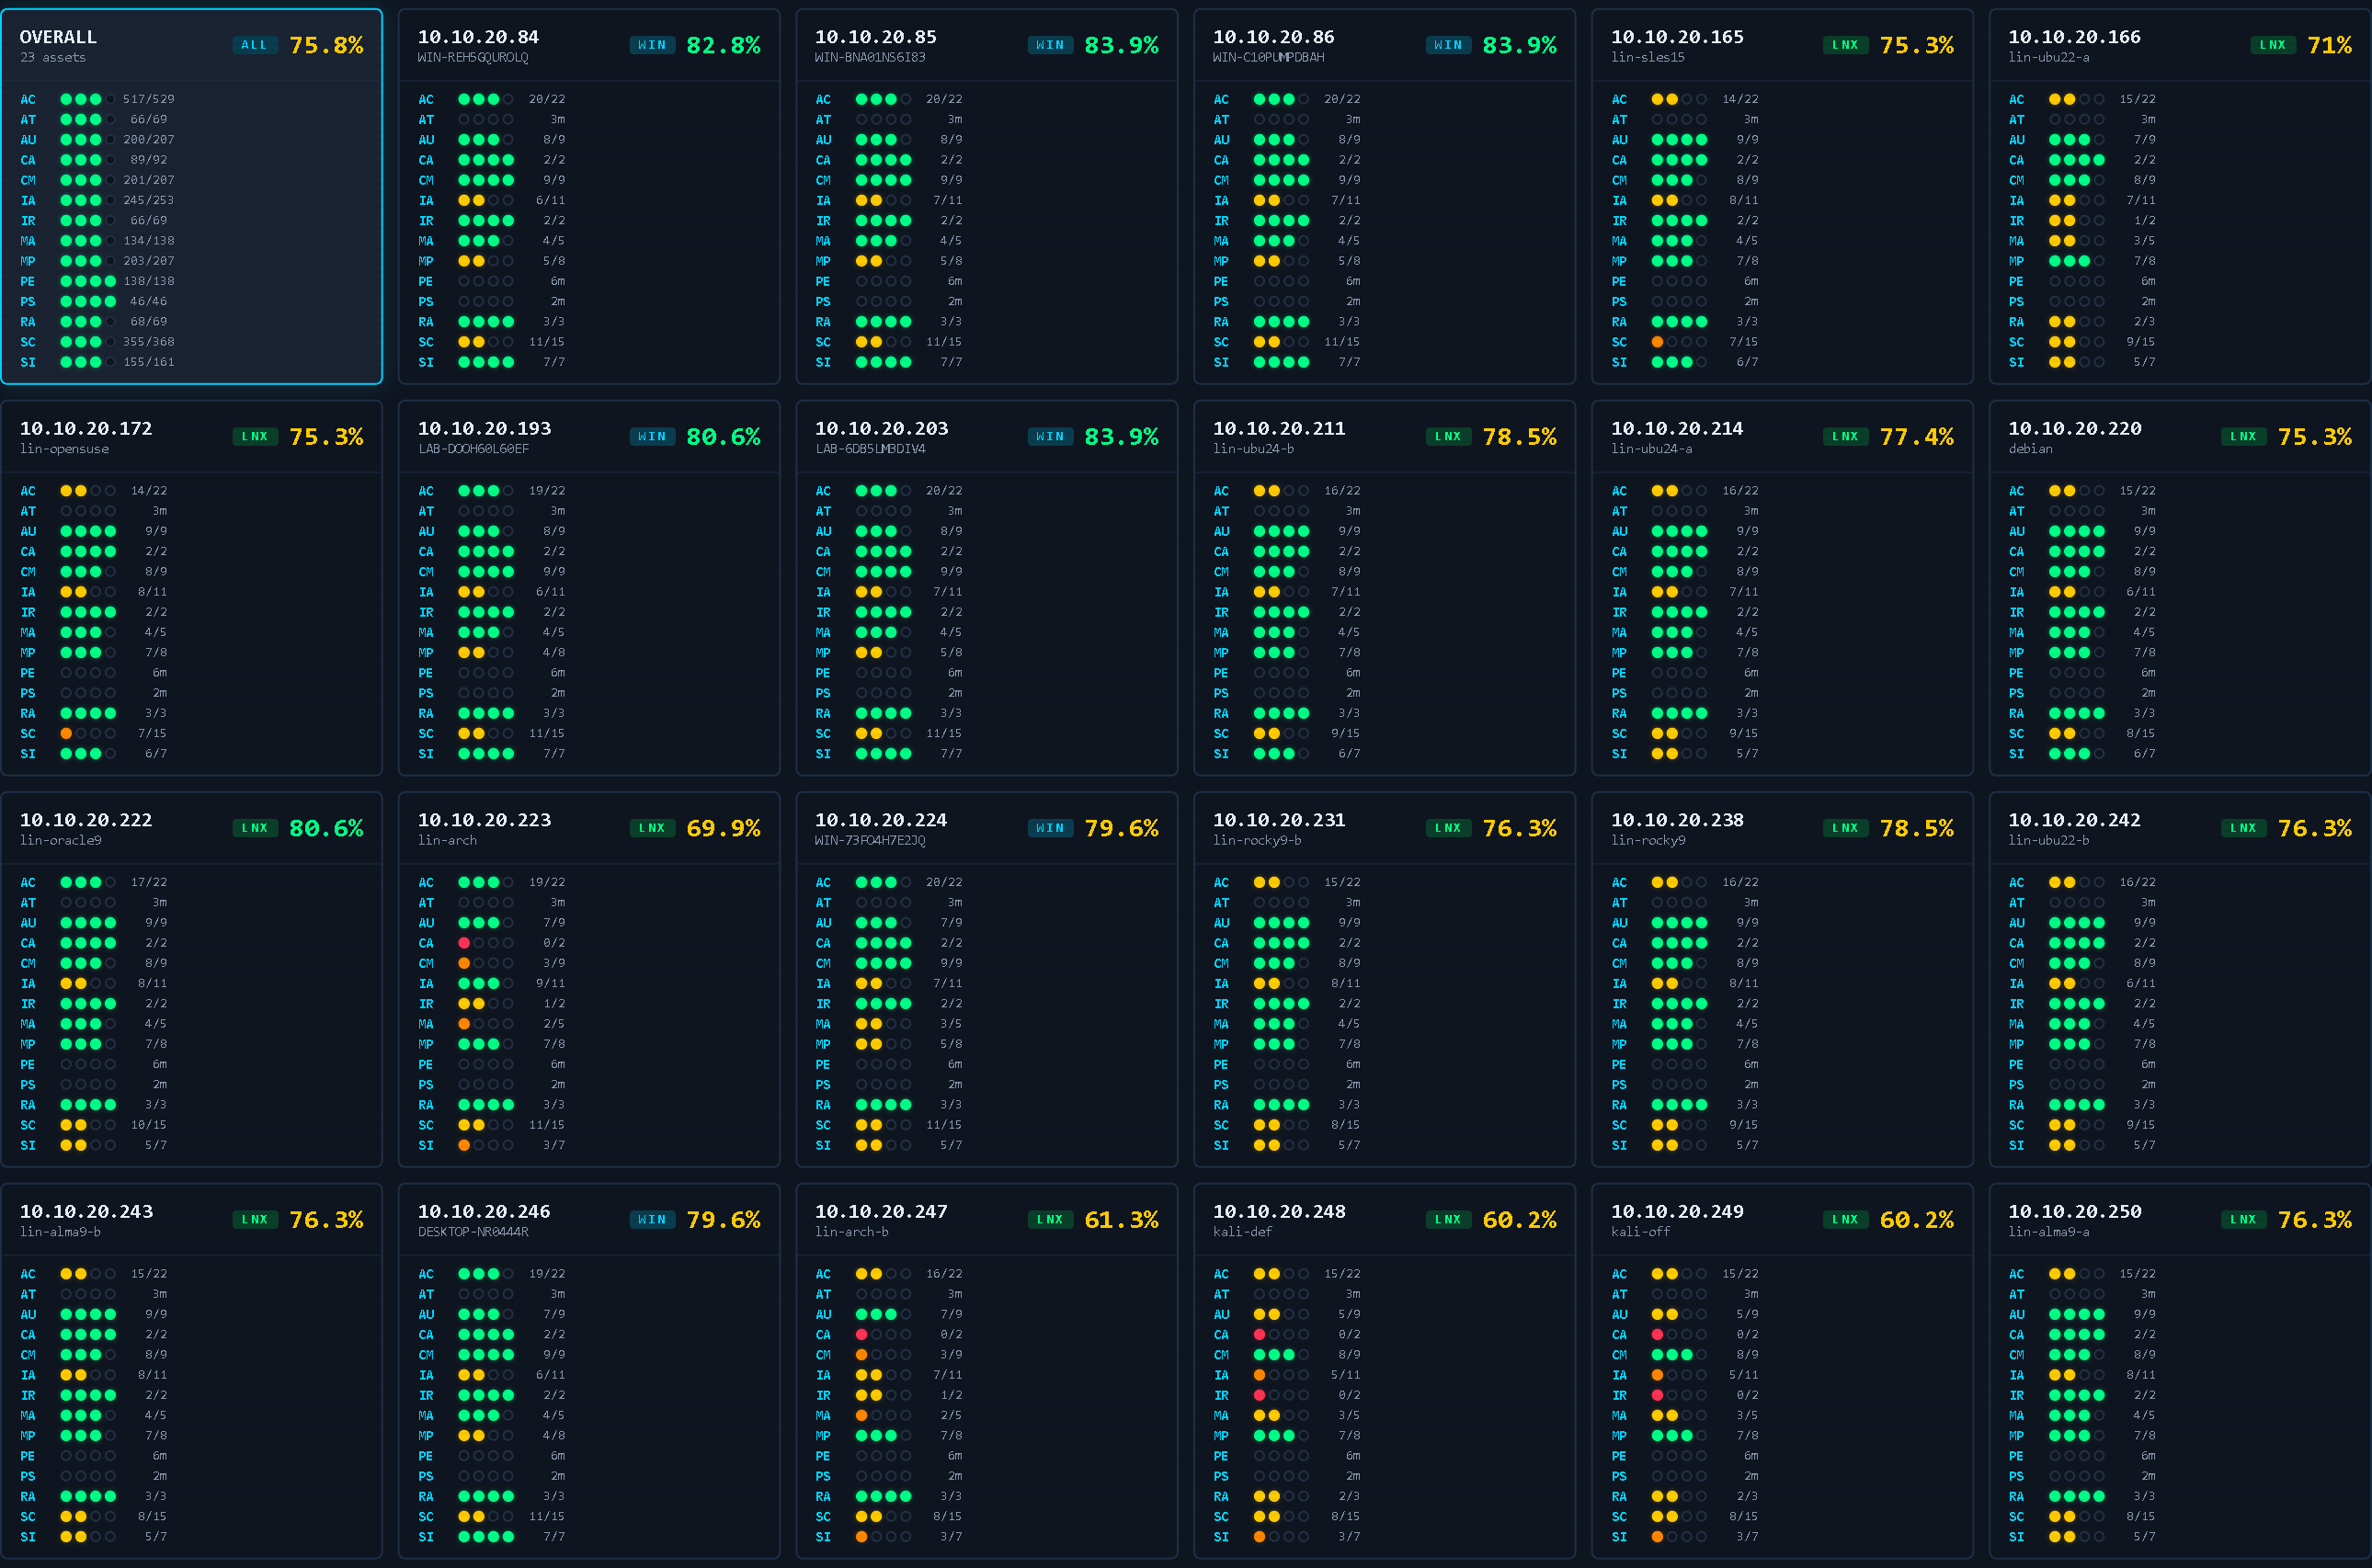
6-Step Guided Workflow
From network discovery through signed evidence collection in 6 structured steps. Zero guesswork — the dashboard guides you through discovery, preparation, scanning, review, remediation, and teardown.
Zero-Credential Scanning
Deploy SSH keys or certificates during endpoint preparation. Admin credentials are entered once — all subsequent scanning and remediation uses deployed keys automatically. After the one-time key deployment, no passwords cross the wire — scanning and remediation use deployed keys/certs.
Guarded Remediation
Smart ordering, lockout detection, rollback bundles, and safety timeouts. The highest-risk lockout control runs last. DANGER MODE for high-risk controls with confirmation overlay and rollback capability.
Signed Evidence Package
23-document evidence package with SHA-256 hashes and Ed25519 digital signatures. Baseline auto-collected after scan, final package after remediation. Both ZIPs submitted to your C3PAO.
Produce Secure Verifiable Evidence with ForteFide
Scanning that produces evidence a C3PAO can independently verify — signed, tamper-evident, and yours — without forcing your operations to revolve around the audit.
Written for C3PAO Assessors
ForteFide ships its own C3PAO Assessor Guide — a document built for the auditor, not the buyer. The signed evidence package contains everything an assessor needs to verify your CMMC posture offline, with no callback to DenseDefense in the trust path.
Wide OS Coverage Out of the Box
11 Linux distributions and 7 Windows distributions tested and supported. No agent install — scanning works against your existing systems as they are.
Right-Sized for Your Environment
Target counts adapt to server size, hardware constraints, and regional spread. Scan a single server or a multi-region fleet without re-architecting the tool around the assessment.
100% Tier 1 Cert Auth — Even Server 2012 R2
Every supported Windows version — including the long-standing Server 2012 R2 holdout — and every Linux family runs scan and remediation under Tier 1 SSH certificate authentication. 30-day per-target certs derived from your license. No persistent admin credential. No long-lived static key.
100% Airgap Operation
The scanner NEVER reaches densedefense.com. Not for packages, not for licenses, not for evidence verification. Sneakernet the .deb in, sneakernet the signed ZIP out. Your CUI never leaves your boundary.
Optional Air-Gap Tooling
Air-gap-constrained environments get the additional tooling they need bundled and ready. Connected environments use the same installer with the air-gap pieces inactive.
Signed Evidence + Standalone Offline Verifier
Every signed evidence ZIP carries an Ed25519 signature, SHA-256 per-artifact hashes, and a standalone Python verifier script. Your assessor verifies the package offline, on their own machine — no DenseDefense callback and no license key required.
Leave-No-Trace Teardown with Rollback Bundle
Every change captures a rollback bundle before it lands, so you can revert what ForteFide changed. An on-target emergency-revert.sh is designed to restore the captured pre-engagement state with no ForteFide, no network, and no hypervisor required. After Teardown, ForteFide removes the deployed service account, keys, and certs it created.
Your Key Stays Yours; the Proof Stands Alone
Your license.key stays on your machine and never travels with the evidence. Each signed package proves itself: the assessor checks its Ed25519 signature and SHA-256 per-artifact hashes offline with the bundled verifier — no license key, no DenseDefense callback. Keep the key private; the proof stands on its own.
Optional Cloud Evidence Vault
For connected environments. Your license key never leaves your machine — the vault stores signed packages, never signing material.
For You
Push completed evidence packages from ForteFide to a per-user vault scoped by license. You retain the license key. The vault holds the artifact, not the proof.
For Your C3PAO
Grant your assessor an engagement-scoped, expiring read link. They download the package and verify it locally with the bundled standalone verifier — offline, no license key and no DenseDefense callback required.
For Airgapped Environments
If your scanner has no internet, the vault is optional. ForteFide produces the same signed package locally for sneakernet handoff to the assessor — chain-of-custody preserved either way.
If You Lose The Key
Lose your license file and your evidence is still good — verification never needed the key. Anyone holding a signed package can still check its Ed25519 signature and per-artifact hashes offline with the bundled verifier. If you also stop using the vault, DenseDefense can revoke its share links so no new downloads are issued; the packages you already hold stay verifiable. After you cancel, we keep your evidence in the vault for 30 days in case you need it, so you can still retrieve it before it is removed. Keep a backup outside the vault.
Protection Layers
8,800+ strings sealed with AES-256-GCM authenticated encryption, keyed by HKDF-SHA256 and bound to the machine. Plaintext exists only in RAM during execution.
Every remediation command encrypted at rest with authenticated encryption.
Offline cryptographic license validation with tamper-evident signatures.
Runtime self-verification of critical files and module structure at startup.